|
SASC
DVBSoftCAM
|
|
SASC
DVBSoftCAM
|
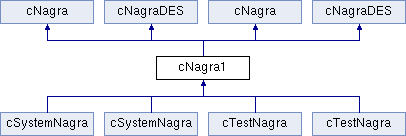
 Inheritance diagram for cNagra1:
Protected Member Functions | |
| virtual void | CreatePQ (const unsigned char *key, BIGNUM *p, BIGNUM *q) |
| bool | DecryptECM (const unsigned char *in, unsigned char *out, const unsigned char *vkey, int len, BIGNUM *e1, BIGNUM *n1, BIGNUM *n2) |
| bool | DecryptEMM (const unsigned char *in, unsigned char *out, const unsigned char *vkey, int len, BIGNUM *e1, BIGNUM *n1, BIGNUM *n2) |
| void cNagra1::CreatePQ | ( | const unsigned char * | key, |
| BIGNUM * | p, | ||
| BIGNUM * | q | ||
| ) | [protected, virtual] |
Implements cNagra.
Definition at line 643 of file nagra1.c.
References cNagraDES::Decrypt(), i, and RotateBytes().
{
  // Make des_key
  unsigned char des_data[32];
  unsigned char des_key[8], des_tmp[8];
  memcpy(des_data,key,8);
  RotateBytes(des_tmp,key,8);
  des_tmp[7]=0x00;
  Decrypt(des_data,des_tmp,des_key,true);
  RotateBytes(des_key,8);
  des_key[7]=0x00;

  // Calculate P
  for(int i=0; i<4; i++) {
    const int off=i*8;
    memcpy(&des_data[off],&key[4],8);
    des_data[off]^=i;
    Decrypt(&des_data[off],des_key,des_tmp,true);
    memcpy(&des_data[off],des_tmp,8);
    }
  BN_bin2bn(des_data,32,p);
  BN_add_word(p,(key[12]<<4)|((key[13]>>4)&0x0f));
  BN_set_bit(p,(BN_num_bytes(p)*8)-1);

  // Calculate Q
  for(int i=0; i<4; i++) {
    const int off=i*8;
    memcpy(&des_data[off],&key[4],8);
    des_data[off]^=(i+4);
    Decrypt(&des_data[off],des_key,des_tmp,true);
    memcpy(&des_data[off],des_tmp,8);
    }
  BN_bin2bn(des_data,32,q);
  BN_add_word(q,((key[13]&0x0f)<<8)|key[14]);
  BN_set_bit(q,(BN_num_bytes(q)*8)-1);
}
| virtual void cNagra1::CreatePQ | ( | const unsigned char * | key, |
| BIGNUM * | p, | ||
| BIGNUM * | q | ||
| ) | [protected, virtual] |
Implements cNagra.
| bool cNagra1::DecryptECM | ( | const unsigned char * | in, |
| unsigned char * | out, | ||
| const unsigned char * | vkey, | ||
| int | len, | ||
| BIGNUM * | e1, | ||
| BIGNUM * | n1, | ||
| BIGNUM * | n2 | ||
| ) | [protected] |
| bool cNagra1::DecryptECM | ( | const unsigned char * | in, |
| unsigned char * | out, | ||
| const unsigned char * | vkey, | ||
| int | len, | ||
| BIGNUM * | e1, | ||
| BIGNUM * | n1, | ||
| BIGNUM * | n2 | ||
| ) | [protected] |
Definition at line 577 of file nagra1.c.
References L_SYS_CRYPTO, mod, PRINTF, cNagra::pubExp, cRSA::RSA(), cNagra::rsa, and cNagraDES::SigCheck().
Referenced by cSystemNagra::ProcessECM().
{
  cBN result;
  if(rsa.RSA(result,&in[2],len,pubExp,n2)<=0) {
    PRINTF(L_SYS_CRYPTO,"error decrypting ECM (round 1)");
    return false;;
    }
  cBN mod;
  BN_set_word(mod,in[0]>>4);
  BN_lshift(mod,mod,508);
  BN_add(result,result,mod);
  if(rsa.RSA(out,64,result,e1,n1,false)!=64) {
    PRINTF(L_SYS_CRYPTO,"error: result of ECM decryption is not 64 bytes");
    return false;
    }
  if(vkey && !SigCheck(out,&out[56],vkey,7)) {
    PRINTF(L_SYS_CRYPTO,"ECM decryption failed");
    return false;
    }
  return true;
}
| bool cNagra1::DecryptEMM | ( | const unsigned char * | in, |
| unsigned char * | out, | ||
| const unsigned char * | vkey, | ||
| int | len, | ||
| BIGNUM * | e1, | ||
| BIGNUM * | n1, | ||
| BIGNUM * | n2 | ||
| ) | [protected] |
Definition at line 599 of file nagra1.c.
References L_SYS_CRYPTO, mod, PRINTF, cNagra::pubExp, RotateBytes(), cRSA::RSA(), cNagra::rsa, and cNagraDES::SigCheck().
Referenced by cSystemNagra::ProcessEMM().
{
  cBN result;
  if(rsa.RSA(result,&in[9],len,pubExp,n2)<=0) {
    PRINTF(L_SYS_CRYPTO,"error decrypting EMM (round 1)");
    return false;;
    }
  cBN mod;
  BN_set_word(mod,in[0]>>6);
  BN_lshift(mod,mod,510);
  BN_add(result,result,mod);
  if(rsa.RSA(out,64,result,e1,n1,false)!=64) {
    PRINTF(L_SYS_CRYPTO,"error: result of EMM decryption is not 64 bytes");
    return false;
    }
  if(!vkey || SigCheck(out,&in[1],vkey,8))
    return true;

  // We need to use signature exchange method (7blocks emm,1 block signature)
  PRINTF(L_SYS_CRYPTO,"warning: signature failed,trying signature exchange method");
  unsigned char buf[8];
  RotateBytes(buf,&in[1],sizeof(buf));
  cBN newdata, newsig;
  BN_bin2bn(buf,sizeof(buf),newdata);
  BN_copy(newsig,result);
  BN_mask_bits(newsig,64);
  BN_bn2bin(newsig,buf);
  RotateBytes(buf,sizeof(buf));

  BN_rshift(result,result,64); // delete the lower 64 bits,we saved it
  BN_lshift(result,result,64); // before as the new 64 bit signature
  BN_add(result,result,newdata);

  if(rsa.RSA(out,64,result,e1,n1)!=64) {
    PRINTF(L_SYS_CRYPTO,"error: result of EMM decryption is not 64 bytes");
    return false;
    }
  if(vkey && !SigCheck(out,buf,vkey,8)) {
    PRINTF(L_SYS_CRYPTO,"fatal: signature failed in signature exchange method");
    return false;
    }
  return true;
}
| bool cNagra1::DecryptEMM | ( | const unsigned char * | in, |
| unsigned char * | out, | ||
| const unsigned char * | vkey, | ||
| int | len, | ||
| BIGNUM * | e1, | ||
| BIGNUM * | n1, | ||
| BIGNUM * | n2 | ||
| ) | [protected] |
 1.7.3