|
SASC-NG
DVBSoftCAM
|
|
SASC-NG
DVBSoftCAM
|
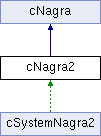
 Inheritance diagram for cNagra2:
Protected Member Functions | |
| virtual void | CreatePQ (const unsigned char *key, BIGNUM *p, BIGNUM *q) |
| bool | DecryptECM (const unsigned char *in, unsigned char *out, const unsigned char *key, int len, const unsigned char *vkey, BIGNUM *m) |
| bool | DecryptEMM (const unsigned char *in, unsigned char *out, const unsigned char *key, int len, const unsigned char *vkey, BIGNUM *m) |
Protected Attributes | |
| cIDEA | idea |
| void cNagra2::CreatePQ | ( | const unsigned char * | key, |
| BIGNUM * | p, | ||
| BIGNUM * | q | ||
| ) | [protected, virtual] |
Implements cNagra.
Definition at line 1146 of file nagra2.c.
References cIDEA::Decrypt(), i, idea, cIDEA::SetEncKey(), and xxor.
{
  // Calculate P and Q from PK
  IdeaKS ks;
  idea.SetEncKey(key,&ks);
  // expand IDEA-G key
  unsigned char idata[96];
  for(int i=11; i>=0; i--) {
    unsigned char *d=&idata[i*8];
    memcpy(d,&key[13],8);
    *d^=i;
    idea.Decrypt(d,8,&ks,0);
    xxor(d,8,d,&key[13]);
    *d^=i;
    }
  // Calculate P
  idata[0] |= 0x80;
  idata[47] |= 1;
  BN_bin2bn(idata,48,p);
  BN_add_word(p,(key[21] << 5 ) | ((key[22] & 0xf0) >> 3));
  // Calculate Q
  idata[48] |= 0x80;
  idata[95] |= 1;
  BN_bin2bn(idata+48,48,q);
  BN_add_word(q,((key[22]&0xf)<<9) | (key[23]<<1));
}
| bool cNagra2::DecryptECM | ( | const unsigned char * | in, |
| unsigned char * | out, | ||
| const unsigned char * | key, | ||
| int | len, | ||
| const unsigned char * | vkey, | ||
| BIGNUM * | m | ||
| ) | [protected] |
Definition at line 1188 of file nagra2.c.
References cIDEA::Decrypt(), i, idea, L_SYS_CRYPTO, PRINTF, cNagra::pubExp, RotateBytes(), cRSA::RSA(), and cNagra::rsa.
Referenced by cSystemNagra2::ProcessECM().
{
  int sign=in[0] & 0x80;
  if(rsa.RSA(out,in+1,64,pubExp,m)<=0) {
    PRINTF(L_SYS_CRYPTO,"first RSA failed (ECM)");
    return false;
    }
  out[63]|=sign; // sign adjustment
  if(len>64) memcpy(out+64,in+65,len-64);

  if(in[0]&0x04) {
    unsigned char tmp[8];
    DES_key_schedule ks1, ks2;
    RotateBytes(tmp,&key[0],8);
    DES_key_sched((DES_cblock *)tmp,&ks1);
    RotateBytes(tmp,&key[8],8);
    DES_key_sched((DES_cblock *)tmp,&ks2);
    memset(tmp,0,sizeof(tmp));
    for(int i=7; i>=0; i--) RotateBytes(out+8*i,8);
    DES_ede2_cbc_encrypt(out,out,len,&ks1,&ks2,(DES_cblock *)tmp,DES_DECRYPT);
    for(int i=7; i>=0; i--) RotateBytes(out+8*i,8);
    }
  else idea.Decrypt(out,len,key,0);

  RotateBytes(out,64);
  if(rsa.RSA(out,out,64,pubExp,m,false)<=0) {
    PRINTF(L_SYS_CRYPTO,"second RSA failed (ECM)");
    return false;
    }
  if(vkey && !Signature(vkey,out,out+8,len-8)) {
    PRINTF(L_SYS_CRYPTO,"signature failed (ECM)");
    return false;
    }
  return true;
}
| bool cNagra2::DecryptEMM | ( | const unsigned char * | in, |
| unsigned char * | out, | ||
| const unsigned char * | key, | ||
| int | len, | ||
| const unsigned char * | vkey, | ||
| BIGNUM * | m | ||
| ) | [protected] |
Definition at line 1224 of file nagra2.c.
References cNagra::CreateRSAPair(), cIDEA::Decrypt(), exp, idea, L_SYS_CRYPTO, PRINTF, cNagra::pubExp, RotateBytes(), cRSA::RSA(), and cNagra::rsa.
Referenced by cSystemNagra2::ProcessEMM().
{
  int sign=in[0]&0x80;
  if(rsa.RSA(out,in+1,96,pubExp,m)<=0) {
    PRINTF(L_SYS_CRYPTO,"first RSA failed (EMM)");
    return false;
    }
  out[95]|=sign; // sign adjustment
  cBN exp;
  if(in[0]&0x08) {
    // standard IDEA decrypt
    if(len>96) memcpy(out+96,in+97,len-96);
    idea.Decrypt(out,len,key,0);
    BN_set_word(exp,3);
    }
  else {
    // private RSA key expansion
    CreateRSAPair(key,0,exp,m);
    }
  RotateBytes(out,96);
  if(rsa.RSA(out,out,96,exp,m,false)<=0) {
    PRINTF(L_SYS_CRYPTO,"second RSA failed (EMM)");
    return false;
    }
  if(vkey && !Signature(vkey,out,out+8,len-8)) {
    PRINTF(L_SYS_CRYPTO,"signature failed (EMM)");
    return false;
    }
  return true;
}
cIDEA cNagra2::idea [protected] |
Definition at line 1139 of file nagra2.c.
Referenced by CreatePQ(), DecryptECM(), and DecryptEMM().
 1.7.3